Key Takeaways
- Antivirus and EDR solve different cybersecurity problems.
- Antivirus helps block known threats before they can execute.
- EDR provides deeper visibility into suspicious endpoint activity and helps detect, investigate, and contain threats.
- Many businesses use antivirus and EDR together as part of a layered security strategy.
- Managed EDR combines endpoint monitoring with human investigation and response support.
- EDR can help organizations reduce operational disruption during cybersecurity incidents by improving visibility and response times.
What Is Antivirus Software?
Traditional antivirus (AV) software is designed to identify and block known malicious files, applications, and behaviors before they can cause damage.
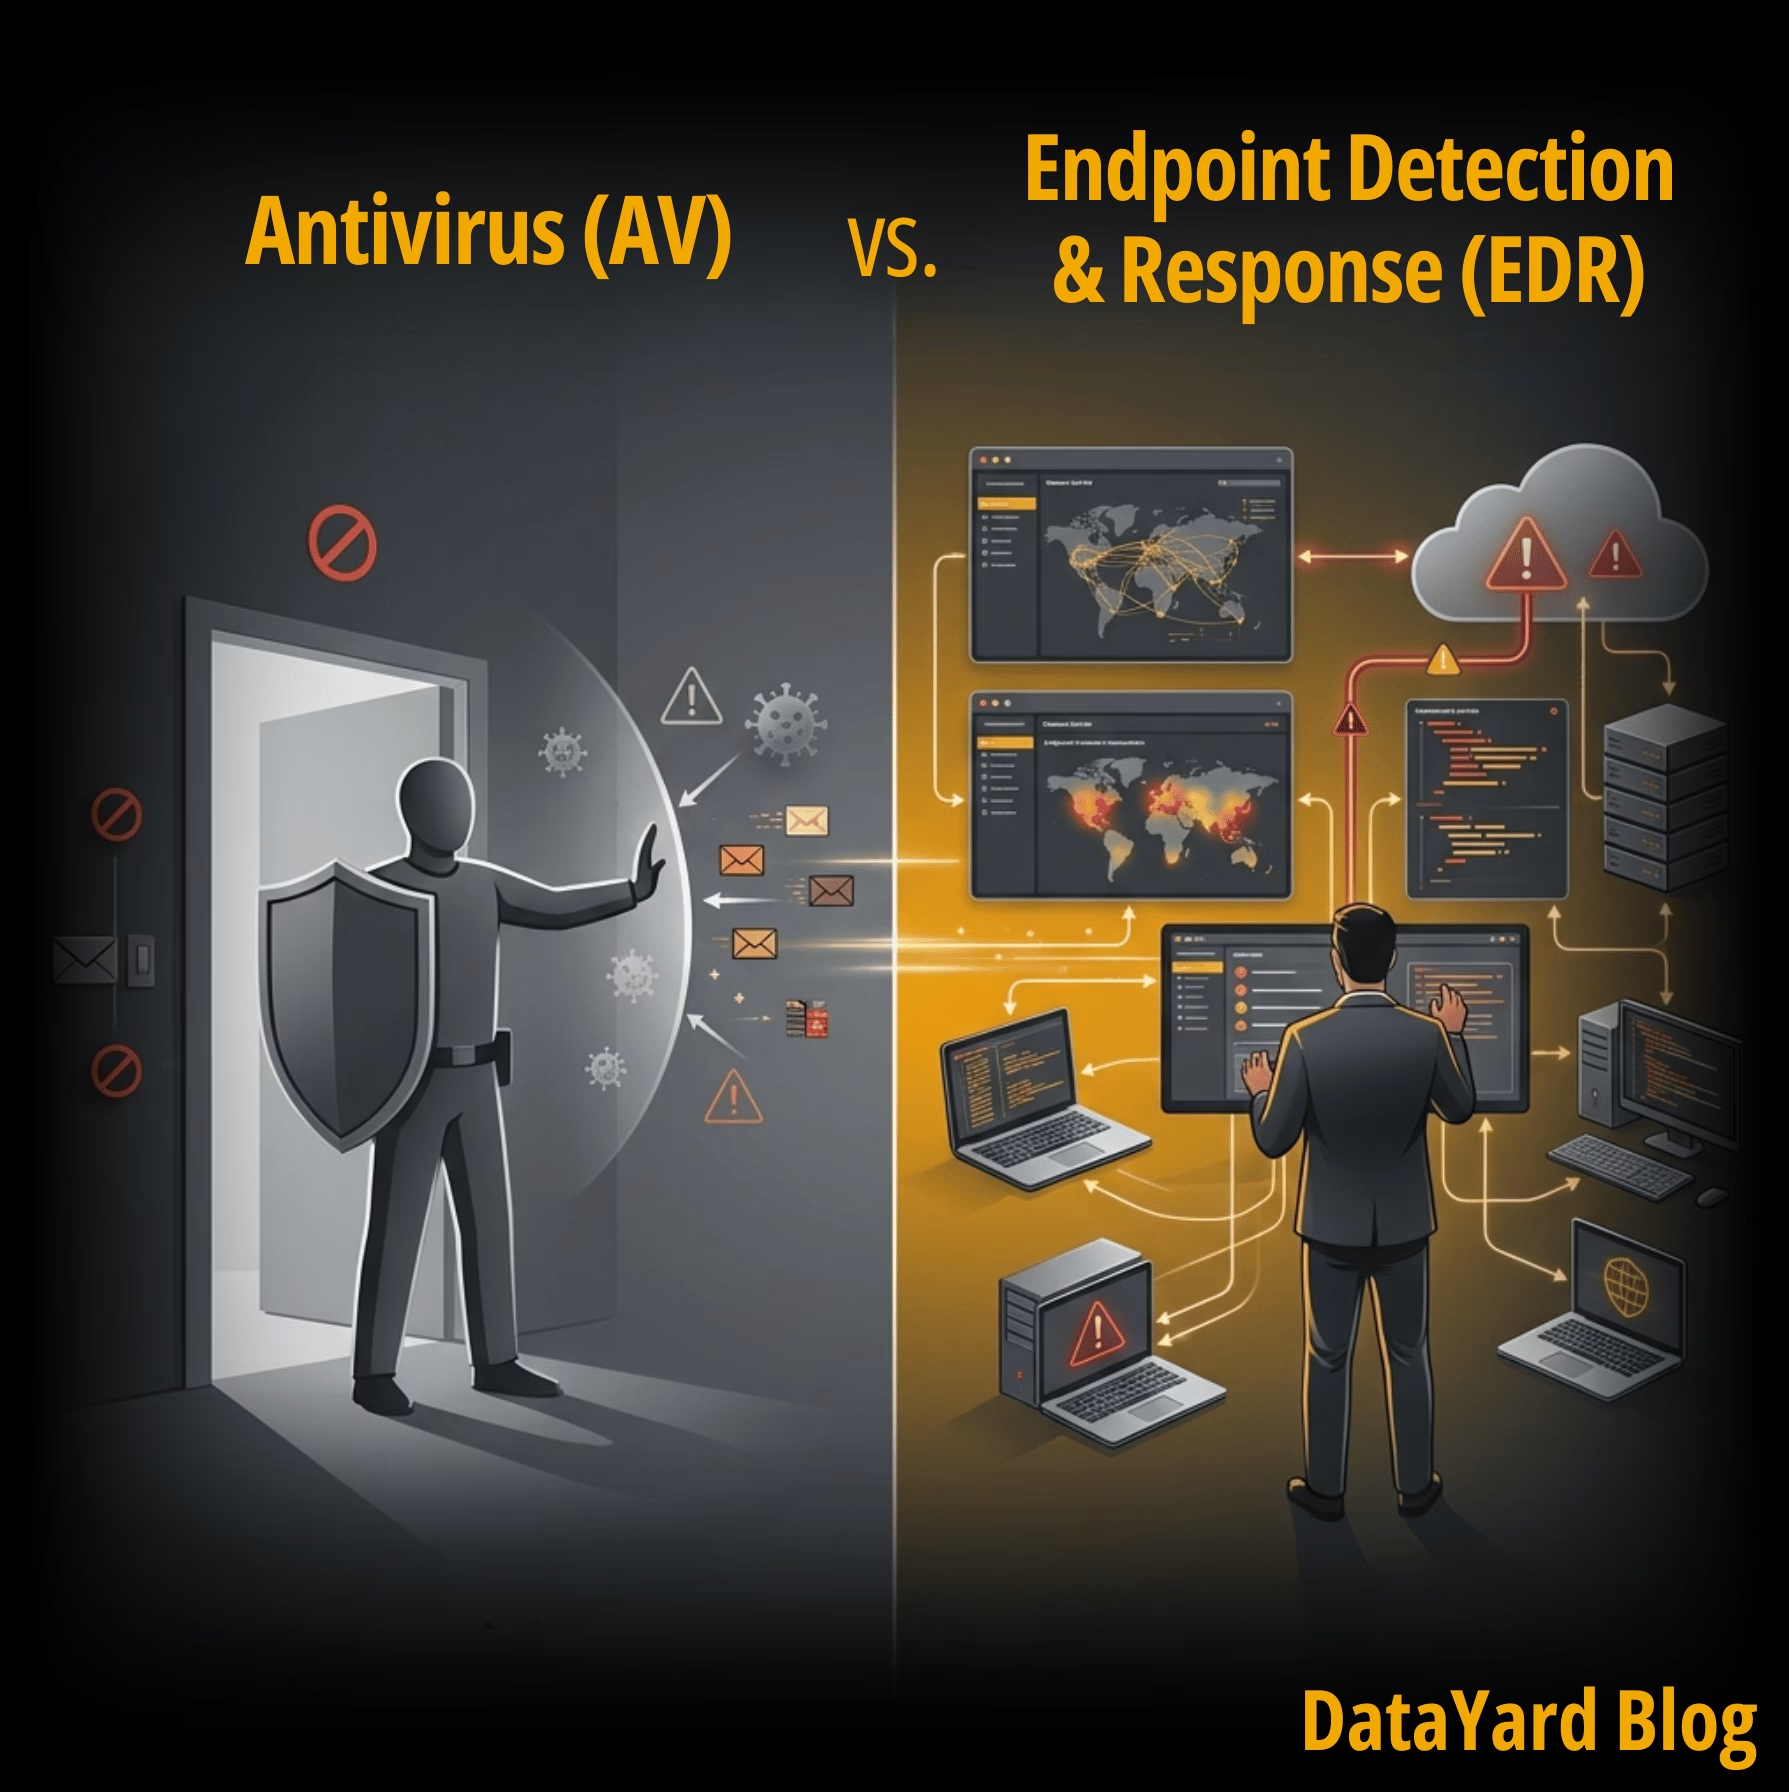
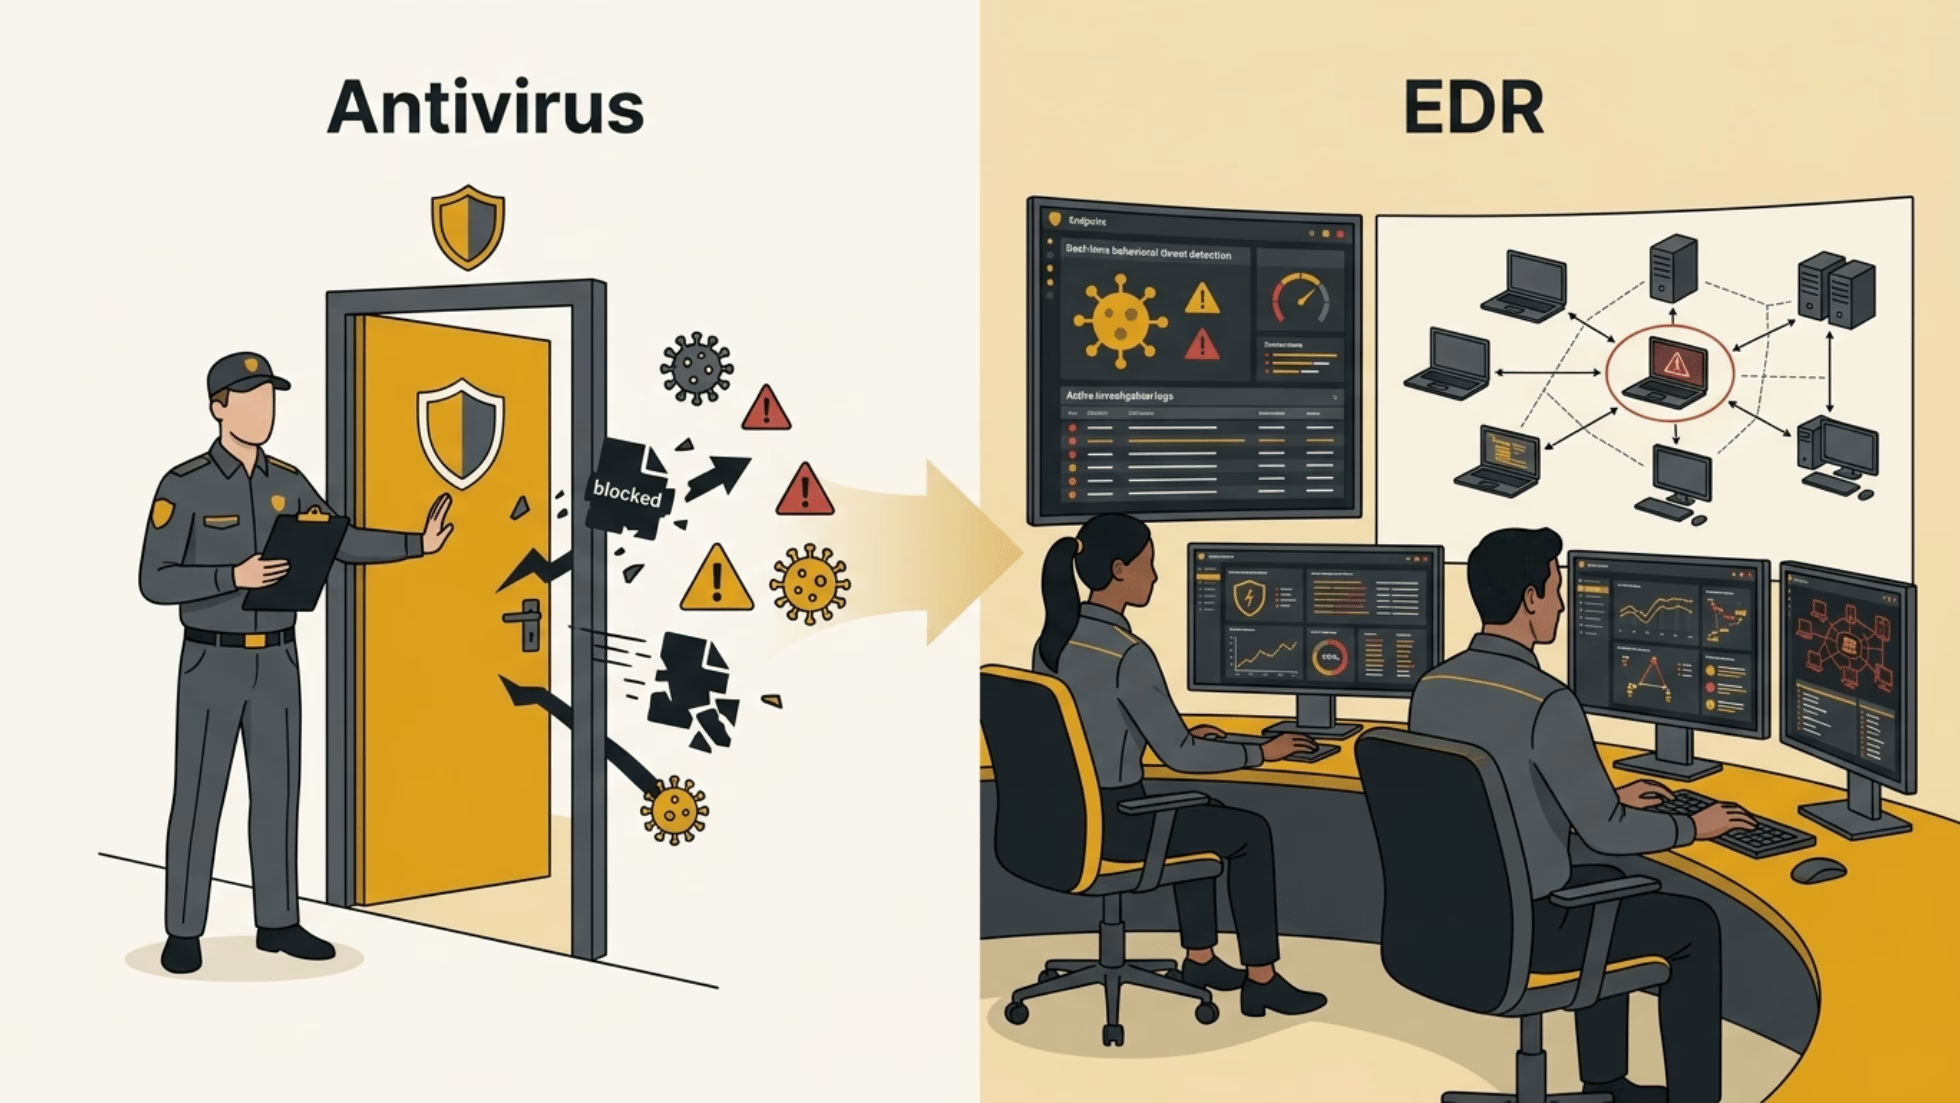
Think of antivirus as a security guard checking IDs at the front door. It knows what threats look like, and it stops the ones it recognizes from getting in.
Modern antivirus platforms have come a long way from their early days and often include features like:
- Malware and ransomware protection
- Web and email scanning
- Behavioral analysis
- Automatic quarantining of suspicious files
For many businesses, antivirus remains an important first layer of defense -- one that’s effective at stopping a wide range of routine, well-known threats.
The limitation is: antivirus is most effective against threats it already recognizes. Newer, more sophisticated attacks that don’t match known signatures can pass through undetected.
What Is Endpoint Detection & Response (EDR)?
EDR goes a step further than antivirus. Rather than focusing on blocking known threats, EDR continuously monitors behavior across your endpoints -- workstations, laptops, servers, and remote employee devices -- and flags activity that looks suspicious based on users' typical working patterns, even if it doesn't match a known signature.
Going back to the security guard analogy: if antivirus is the guard checking IDs at the door, EDR is the broader security team monitoring cameras throughout the building, investigating anything that looks off, and responding when something abnormal happens -- even after someone’s already inside.
EDR platforms give organizations the ability to:
- Detect unusual or suspicious behavior in real time
- Investigate incidents quickly with full context
- Isolate affected systems before threats can spread
- Reduce lateral movement across a network
- Respond faster when something goes wrong
Fast response times matter more than many businesses realize. The window between when a threat is detected and when it’s contained can be the difference between a minor incident and days of downtime.
Why EDR Is Becoming More Important
Cybersecurity threats have become increasingly focused on endpoints, including the workstations, laptops, and servers your employees use every day.
According to Huntress, attackers frequently rely on legitimate administrative tools, stolen credentials, remote access software, and “living off the land” techniques that may not appear malicious to traditional antivirus software alone. These types of attacks are designed to blend in, and that’s exactly what makes them so difficult to catch with prevention-only tools.
It’s one of the main reasons EDR adoption has grown significantly in recent years. Rather than relying solely on known malware signatures, EDR helps organizations identify suspicious behaviors and investigate unusual activity that may indicate compromise.
Modern EDR platforms can also help reduce response times by:
- Alerting IT teams to suspicious activity quickly
- Providing behavioral visibility into endpoint activity
- Isolating affected devices during active incidents
- Supporting faster investigation and remediation
For businesses with remote employees or operationally-critical systems, that improved speed and visibility can make a meaningful difference in how disruptive a security incident ends up being.
Huntress reports that 89% of users agree that Managed EDR stopped a threat that would have otherwise significantly impacted their business -- a strong indicator of why managed detection is becoming a go-to addition for lean IT teams.
EDR vs. Antivirus: Key Differences
While both tools improve endpoint security, they work differently and serve different purposes.
Antivirus focuses on prevention. It’s built to block known malicious files and activity before they execute -- quietly, automatically, and with minimal input needed from your team.
EDR focuses on visibility and response. It’s built to a) catch what slips past those initial prevention layers, b) give your team the context to understand what happened, and c) provide the tools to contain it and remediate the issue quickly.
Antivirus is largely automated. It runs in the background and handles routine threats without a lot of end-user investigation. As long as your AV service is installed and kept up-to-date, there isn't much involvement required from IT.
EDR provides deeper investigation capability. EDR platforms typically include threat timelines, behavioral monitoring, forensic visibility, and containment features -- tools that help IT teams understand the full scope of an incident, not just an alert that "something happened".
Neither tool is a complete security strategy on its own. Together, they cover a much broader range of threats.
| Feature | Antivirus | EDR |
|---|---|---|
| Blocks known malware | Yes | Yes |
| Behavioral monitoring | Limited | Extensive |
| Threat investigation tools | Minimal | Advanced |
| Endpoint isolation | Usually No | Yes |
| Detects suspicious activity | Limited | Yes |
| Incident response support | Minimal | Strong |
| Visibility into endpoint activity | Limited | Detailed |
| Best for | Prevention | Detection & Response |
Not sure if your current security stack has the right coverage? DataYard can help you assess where antivirus and EDR fit into your environment. Contact us or explore DataYard’s cybersecurity services.
Why Many Businesses Use Both
Cybersecurity rarely comes down to a single tool. Most strong security setups are built in layers, and antivirus and EDR are designed to cover different parts of that stack:
- Prevention -- Stopping known threats before they execute (Antivirus)
- Detection -- Identifying suspicious activity that bypasses prevention (EDR)
- Investigation -- Understanding what happened and how far it spread (EDR)
- Response -- Containing the threat and limiting damage (EDR)
In many cases, antivirus handles routine threats before they ever become incidents. But when something more sophisticated slips past antivirus and firewall protections -- and it does happen -- EDR provides the visibility needed to catch it quickly and limit the damage.
For organizations with remote employees, growing infrastructure, or operationally critical systems, that additional visibility isn’t a nice-to-have; it's what separates a contained incident from a serious disruption.
Frequently Asked Questions About EDR vs. Antivirus
For most businesses, EDR does not completely replace antivirus. Antivirus remains an important first layer of defense for blocking known threats, while EDR adds visibility, investigation, and response capabilities for suspicious activity that bypasses traditional protections.
Antivirus focuses primarily on prevention by identifying and blocking known malicious files or behaviors. EDR focuses on detecting suspicious activity, investigating incidents, and helping IT teams contain threats that may already be active inside an environment.
Many small and midsize businesses benefit from EDR, especially organizations with remote employees, sensitive data, operationally critical systems, or limited internal IT resources. EDR can help improve visibility and reduce response times during cybersecurity incidents.
EDR platforms can often identify behaviors associated with ransomware activity, such as unusual encryption processes, privilege escalation, or lateral movement. Many EDR tools also include containment features that help isolate affected systems before threats spread further.
Yes. Many organizations run EDR alongside traditional antivirus software as part of a layered security approach. Antivirus helps prevent known threats, while EDR adds detection and response capabilities when suspicious activity occurs.
EDR solutions typically monitor endpoints such as desktop workstations, laptops, servers, remote employee devices, and virtual machines. Some platforms also provide visibility into cloud-hosted systems and hybrid environments.
Response times vary depending on the platform and monitoring setup, but many managed EDR solutions can automatically isolate affected systems and alert security teams within minutes of detecting suspicious activity.
Managed EDR combines Endpoint Detection & Response technology with active human monitoring and response support from cybersecurity professionals. Instead of handling every alert internally, businesses receive help investigating suspicious activity and responding to threats more quickly.
Many small and midsize businesses use managed EDR because they do not have dedicated internal security teams monitoring endpoint activity 24/7. Managed EDR can improve visibility, reduce response times, and help organizations respond more effectively to cybersecurity incidents.